

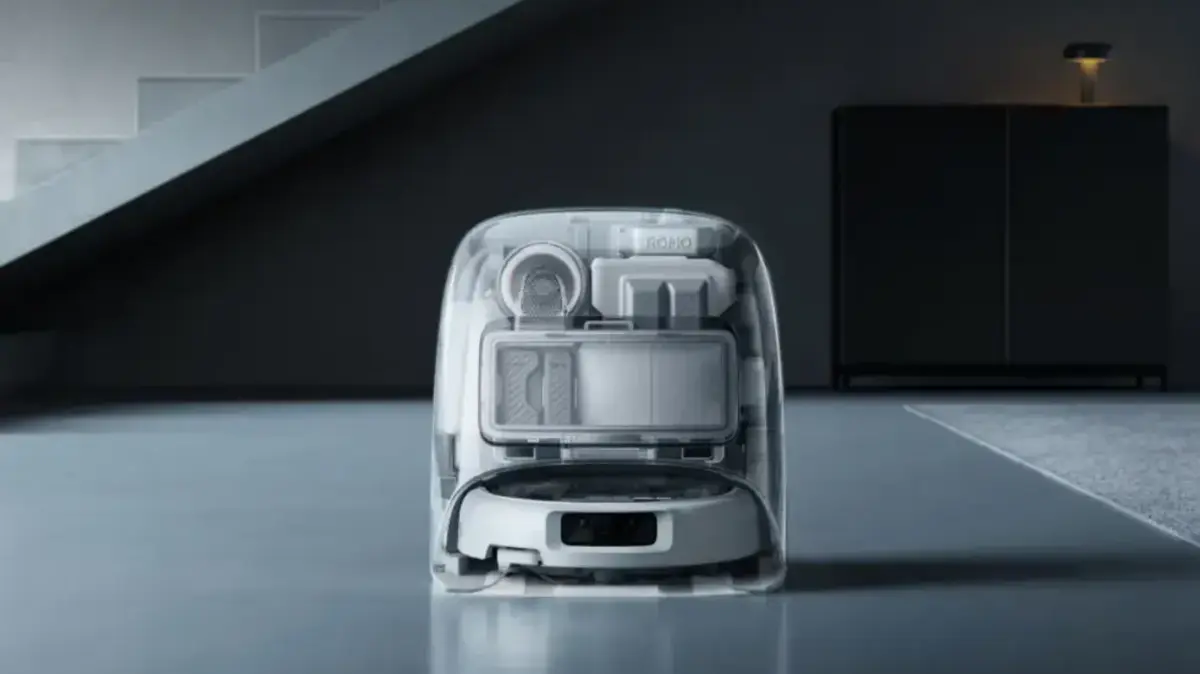
Many Romo units were (very briefly) turned into infiltrators remotely controlled from the other side of the world.
Credit: DJI
A fresh new outrage is circulating through the popular media right now, refocusing attention on the sheer number of connected devices entering modern homes.
It’s focused on a story, first reported by The Verge, in which a Spanish researcher attempted to do some homebrew hacking on his DJI Romo robovac, but instead unintentionally took control of thousands of units worldwide.
Sammy Azdoufal’s original goal was to make his own Romo device directly controllable with his PlayStation 5 controller—which would have made for a fun project, if it had gone to plan. Instead, he found that when his homebrew control app contacted DJI’s servers, what returned was data from thousands of Romo units.
Azdoufal could remotely control all of these units, or a specific one, and see their live camera feeds. He could access the complete 2D floor plan generated by the robot for its own navigation and see its approximate location via its IP address.
Eventually, he went to the media to turn his discovery into an expose, and a DJI quickly patched out the problem. And yes, he eventually got his Romo unit (only his unit, mind you) working with his PS5 controller.
The overall situation may be shocking, but it shouldn’t be surprising; after all, more cybersecurity vulnerabilities are being discovered each quarter than ever before. The much-ballyhooed Internet of Things (IoT) has introduced an incredible number of connected devices, and each one is a potential security risk. One study even found that newly published vulnerabilities are often exploited within a day of being revealed.
This problem is often blamed on outdated tech, with people still using devices that are no longer supported with software updates, but DJI’s Romo was a brand-new product. The company believes that the vulnerability involved a “backend permission validation issue affecting MQTT-based communication between the device and the server.”
As we all know, home networks are often as secure as their least-secure connected device, allowing sophisticated hackers to compromise one device, which makes it easier to attack other networked devices.
The most frequently compromised devices are still computers, but that’s because they’re also most exposed to threats; the most vulnerable per encounter are lower-priced gadgets that just happen to require access to your WiFi network.
It should be noted that DJI has a pretty solid reputation for quality in its releases, especially for a rapid-prototyping company. I think this most likely represents the fall in quality control that happens when a specialist camera-drone company tries to branch out enough to become China’s answer to General Electric in the 1980s.
